



AI-Generated Code Audit, Rescue & Production Hardening
Built your app with Cursor, Lovable or Bolt? Peiko engineers run an ai code security audit, fix what they find and get your app ready for real users.
IS YOUR AI-BUILT APP READY FOR PRODUCTION?
An ai code security audit is the fastest way to find out. Independent tests show why it matters: in Veracode’s 2026 study, about 44% of AI code-generation tasks produced code with a security flaw, even though the code compiled. These are the typical signs that an app needs a review before launch:
SECURITY GAPS
API keys or passwords sit in the code, and endpoints return or change data without checking who is asking.
NO SAFETY NET
There are no automated tests, so every change is checked by hand, and new features break old ones.
PERFORMANCE LIMITS
Pages slow down as more people sign up, and the database is the first thing to struggle.
HARD TO HAND OVER
Most logic lives in a few huge files, nobody can explain how the app works, and there is no documentation.
OUR AI-GENERATED CODE AUDIT & RESCUE SERVICES
AI-Generated Code Audit
A full ai generated code audit of architecture, code quality, dependencies and data model. You receive a written report with findings ranked by risk and effort.
AI Code Security Audit
Authentication, access control, exposed secrets, injection risks, open APIs and vulnerable packages, checked against the OWASP Top 10. Every issue lands on a fix list sorted by severity.
Code Refactoring & Cleanup
Our ai code refactoring services split oversized files, remove duplicated logic and give the code a structure a development team can work with.
Testing & QA
Automated tests for login, payments and other critical flows, plus regression checks. Testing ai generated code this way stops new features from breaking old ones.
Production Hardening
Separate environments, CI/CD, hosting, monitoring, logging, backups and error handling: the parts AI tools rarely set up, and the parts that keep an app online.
Scaling & Performance
Database design, indexes, caching and load testing, so the app keeps responding when ten users become ten thousand.
App Rescue & Handover
Stuck halfway? Engineers take over a stalled or broken AI-built app, finish the features, write the documentation and stay on as a dedicated team if needed.
WHAT OUR AI CODE AUDIT COVERS
Security
Login, roles, secrets, input handling and OWASP Top 10 risks. You get a severity-ranked fix list.
Architecture
How modules, services and data flows fit together. You get a map of what to keep and what to restructure.
Code Quality
Duplication, file size, naming and dead code. You get a list of refactoring priorities.
Data & Database
Schema, indexes, migrations and data access rules. You get fixes for slow queries and data leaks.
Dependencies
Outdated and vulnerable packages, licenses and unused libraries. You get an update plan.
Testing
Existing tests and coverage of critical flows. You get a test plan for the gaps.
Deployment & Infrastructure
Environments, CI/CD, hosting, backups and access to servers. You get a production-readiness checklist.
Performance
Response times, load behavior and caching. You get the bottlenecks to fix before growth.

HOW AN AI-GENERATED CODE AUDIT WORKS
Since 2017, our software creation team has consistently delivered industry-focused development services that get results.

FIX, REFACTOR OR REBUILD?
The audit decides, not a preference for rewriting. Each part of the app is judged on three questions: is it secure, can a team maintain it, and will it hold up under real load. In our experience, most AI-built apps need targeted fixes and refactoring in a few modules, not a rebuild. Sometimes the honest answer is to keep the AI-written code as it is.
Fix
When the structure is sound and the problems are specific: an open endpoint, a leaked key, a missing check. Fixes take days and carry little risk.
Refactor
When the app works but is hard to change: huge files, copy-pasted logic, no tests. Work goes module by module over weeks, while the app keeps running.
Rebuild a Module
When a part is unsafe or cannot scale, such as payments or the data model. Only that module is rebuilt, with a migration plan, so the rest of the app stays.
HOW MUCH DOES AN AI CODE AUDIT COST?
Audit Only
$1,500 – $4,000 Security, architecture and code quality review with a ranked findings report and a fix plan.
Audit + Security Fixes
$4,000 – $12,000 The audit, then every critical and high-severity security issue fixed, tested and deployed.
Audit + Production Hardening
$8,000 – $25,000 Security fixes plus CI/CD, monitoring, backups, tests for critical flows and performance work.
OUR CASE STUDIES
A scalable GRC platform that automates governance, risk, and compliance.
A comprehensive GRC platform designed to help organizations manage governance, risk, and compliance through automated workflows and centralized processes.


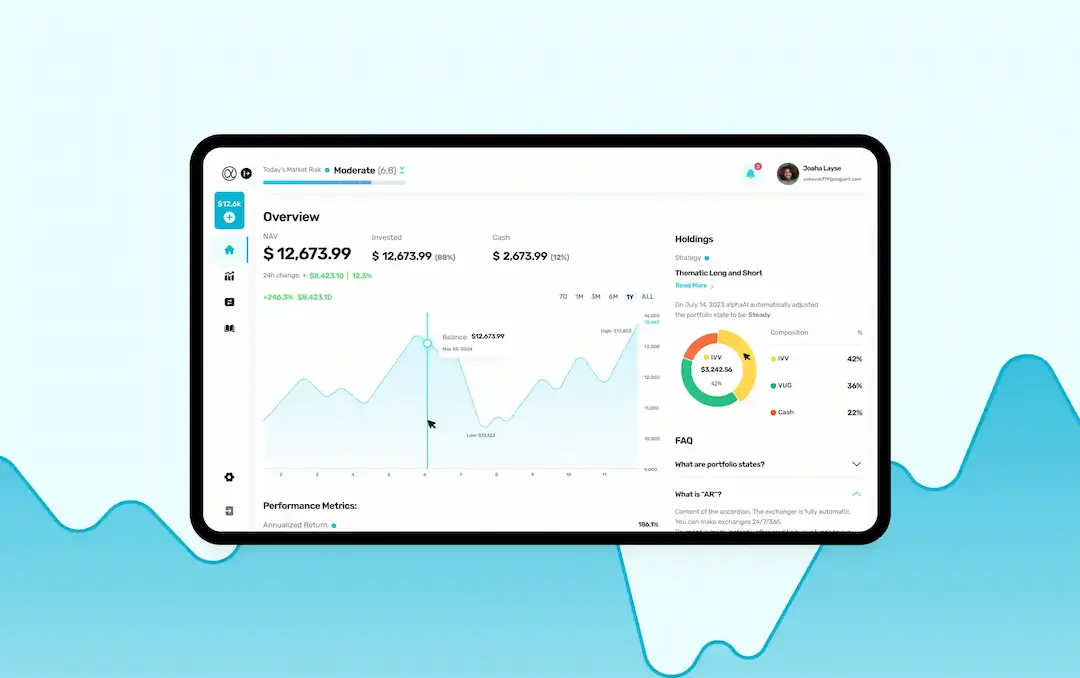
A next-generation AI-powered trading platform that lets retail investors build, simulate, and run fully-automated ETF strategies.
We had to create a secure, real-time trading product from scratch, translate a complex vision into a clear roadmap, and keep development agile enough to absorb regular startup pivots.


Innovative SaaS solution that allows companies to accelerate payments from customers.
The Riabu software helps companies of all sizes – from big enterprises to small businesses – providing them with information about the past payment behavior of potential clients and merchants.


Dipper – a reliable сrowdfunding platform that enables investors and entrepreneurs to raise cash.
This fintech investment platform we developed includes complex strategies with exceptionally precise calculations and the latest functionality.


WHY PEIKO FOR AN AI CODE AUDIT
Production Software Since 2017
Fintech platforms, exchanges and compliance systems have taught our engineers what breaks in production and what attackers look for first.
85+ Engineers, One Team
Backend, frontend, QA and DevOps specialists review your code together, so security, tests and deployment are checked by people who do this daily.
Security-Heavy Projects
Role-based access, audit trails and data isolation are standard in our fintech and RegTech work, like the GRC platform built for a client in Saudi Arabia.
Honest Triage
The audit report says what to keep, not only what to change. If the AI-written code is good enough, you will hear that too.
Rated 5.0 on Clutch
150+ verified reviews and a 100% Job Success score on Upwork reflect consistent delivery for founders and product teams.
Engagement Models
Let’s talk-
Build a long-term engineering team fully focused on your product. We assemble specialists who work as an extension of your in-house team, providing continuous development, product evolution, and technical expertise.
Best for
Long-term product development, startups, SaaS platforms, enterprise products.
-
Ideal for projects with evolving requirements where flexibility is essential. Development priorities can change throughout the project while maintaining complete transparency over scope, progress, and budget.
Best for
Complex software products, AI solutions, digital transformation projects.
Suitable for projects with clearly defined requirements, timelines, and deliverables. We prepare a detailed project scope before development begins to provide predictable budgeting and delivery.
Best for
MVPs, internal business tools, corporate portals, proof of concept.
Start with a structured discovery phase to validate your idea, define technical requirements, estimate development costs, select the optimal technology stack, and create a product roadmap before full-scale implementation.
Best for
New software products, startups, enterprise innovation initiatives.
What Our Clients Say
We don’t just build software, we build success stories

Peiko delivered a smart contract that was highly evaluated by one of the most demanding auditors on the market. They contributed strategically, offering insights that extended far beyond technical development.
Amazing agency, perfect communication and execution (agile development with very high quality of work), they think out of the box and really help you shape the product. They also have great design skills in the team and are always available- I highly recommend them and will definitely hire again for a next big project!
We are pleased that we selected Dima and Peiko as our software development Advisor and partner. Dima and Peiko team beyond the great technical skills, their collaborative approach and project management make them a reliable tech partner.
I selected Peiko team based on their profile and the submitted quality proposal. I also met them personally, and I reached the initial concusion that I am working with a professional team. The end product was delivered with superb quality and structure. the documentaiton part was also great.

If you’re looking to partner with a team that truly understands your vision and has the technical prowess to bring it to life, Peiko is the partner you can rely on.
I consider Peiko a qualified technical partner for many reasons, such as delivering milestones on time, providing fast software improvements, and resolving bug issues quickly. They’re very experienced in blockchain and financial services and get deeply involved in the development process.
What impresses me most about Peiko is their innovative approach! Thanks to Peiko’s efforts, the client has noticed an increase in user engagement and trading volume. The team establishes a seamless workflow by being highly responsive and dedicated to the project. Moreover, they continue to impress the internal team with their innovative solutions.
Their rapid response to our requests was a major factor in the project’s successful completion. Peiko’s efforts have increased user engagement and transactions, meeting expectations. Peiko’s responsive and communicative approach has resulted in a successful partnership. The team is committed to creating a secure and user-friendly platform that caters to auctioneers and buyers.
Peiko has provided deliverables on time and with minimal revisions. The team is responsive to the client’s needs, addresses questions quickly, and consistently delivers items within expectations. Peiko’s communication and problem-solving skills have been remarkable throughout the engagement.
Although the platform has yet to launch, Peiko is able to execute and manage the platform successfully. A collaborative team, they have engaged with the clients to work out the stages and concept in the development of the project. They have communicated well to provide progress updates and feedback.

Although the platform has yet to launch, Peiko is able to execute and manage the platform successfully. A collaborative team, they have engaged with the clients to work out the stages and concept in the development of the project. They have communicated well to provide progress updates and feedback.
They’re an open-minded team and I’m glad to be working with them. Peiko works fast and pays great attention to detail. Regular and honest communication benefit the collaborative partnership. Customers can expect to work with a professional and open-minded team.

My initial trepidation in hiring an agency in another time zone, and a market I was not familiar with, proved unfounded. Always professional. Incredibly switched on. I get the sense they actually really understand what we are trying to achieve. I don’t have to explain everything – they intuitively seem to understand. The designs the team have come up with are fantastic.
We’ve earned a 100% Job Success score on Upwork as a result of consistent delivery, long-term client satisfaction, and predictable results.
View work historyOur work is rated 5.0 on Clutch, reflecting verified client reviews, strong professionalism, and a clear focus on scalable, business-driven digital solutions.
Read reviews WHAT IS AN AI CODE SECURITY AUDIT?
An ai code security audit is an independent review of an app written fully or partly with AI coding assistants. Engineers check authentication, data access, secrets, dependencies and infrastructure, then rank every issue by risk. AI tools write working code quickly, but they often skip the checks a reviewer would insist on. IOActive’s April 2026 study found that 31.6% of AI-generated code samples were fully exploitable. The audit closes that gap before real users and real data arrive.
LAUNCH WITH CONFIDENCE
Find and fix security holes, missing tests and weak spots before the first paying users sign up.
TAKE OVER WITHOUT GUESSWORK
Get a clear map of an inherited AI-written codebase, so a new team knows what it owns on day one.
FAQ
It is a paid review that tells you what to fix before launch. Peiko’s ai generated code review services deliver three things: a findings report ranked by severity, an effort estimate for each issue, and a fix plan that says what to keep, refactor or rebuild. You can act on it with our team or your own.
Not by default. AI tools produce code that runs, but they often skip access checks, input validation and safe handling of secrets. AI-generated code security depends on review and testing, the same as code written by people. Some apps pass an audit with minor fixes; others have critical gaps.
Check for secrets in the code, open API endpoints, missing tests, very large files and slowdowns as users grow. If you see two or more of these, or nobody can explain how the app works, get a review first. Learning how to make ai generated code production ready starts with knowing what is missing.
Yes. The tool matters less than the stack it produced, usually React or Next.js with Node.js, Python or a hosted backend such as Supabase or Firebase. If you need to fix ai generated app issues or hire developer to fix vibe coded app problems, Peiko engineers work directly in your repository.
A typical audit takes 5–10 business days and costs $1,500–$4,000 for a standard AI-built web app. The price depends on codebase size, the number of integrations such as payments, auth and AI APIs, compliance needs, and whether our team continues development after the audit. The fee is fixed before the audit starts.
Usually not. Most AI-built apps need targeted fixes and refactoring in a few modules. A module is rebuilt only when it is unsafe or cannot scale, and the audit explains why. Moving an ai prototype to production rarely requires starting over.
Read-only repository access is enough for the audit. Production data is not needed in most cases; when it is, access is limited, logged and removed after the work. An NDA is signed before any access, and credentials are never stored in shared tools.
Yes. After the ai code security audit and fixes, the same engineers can stay on as a dedicated team, adding features, ai code testing and monitoring. You can also take the report and the documentation to your own developers.
Got a question? Drop us an email at hello@peiko.space